Identify security gaps and strengthen the systems your business relies on. Cantabridge Technologies reviews applications, servers, networks, and access controls, then helps implement and check the improvements your environment needs.
Discuss Your Security RequirementsOur Perspective
Understand the Gaps. Know What to Address First.
An application may expose information to the wrong user. A server may have services open that it no longer needs. An administrator account may retain access after responsibilities change. These are the kinds of issues a focused review can bring into view.
We assess the agreed systems, explain the findings, and prioritize changes around business impact. The work connects assessment with implementation so your team understands both the issue and the next step.
What We Deliver
Security Reviews with Practical Implementation Support
We scope the review around your environment and the questions you need answered. Services can include identifying configuration gaps, reviewing application behavior, implementing approved changes, and checking the results.
Security Assessment
Review the agreed systems and operating practices, document findings, and recommend priorities for improvement.
Application & API Review
Examine selected authentication, authorization, input handling, dependencies, and data-access behavior.
Network & Firewall Review
Review exposed services and connection rules, then define changes around the communication your systems need.
Server & Infrastructure Hardening
Improve agreed server settings, administrative access, permissions, and unnecessary service exposure.
Identity & Access Controls
Review user and service access, role permissions, and the process for granting and removing privileges.
HTTPS & TLS Configuration
Review certificate setup, HTTPS behavior, and renewal arrangements across the agreed services.
Security Logging & Alerts
Configure selected event logs and alerts, with recipients and review responsibilities defined.
Remediation & Follow-Up
Implement approved fixes, recheck the affected areas, and document remaining work or limitations.
Security Services in Practice
Focus on the Systems and Access That Matter
A review can cover a specific concern or a defined part of your environment. These examples show the work we can assess and scope with your team.
 01
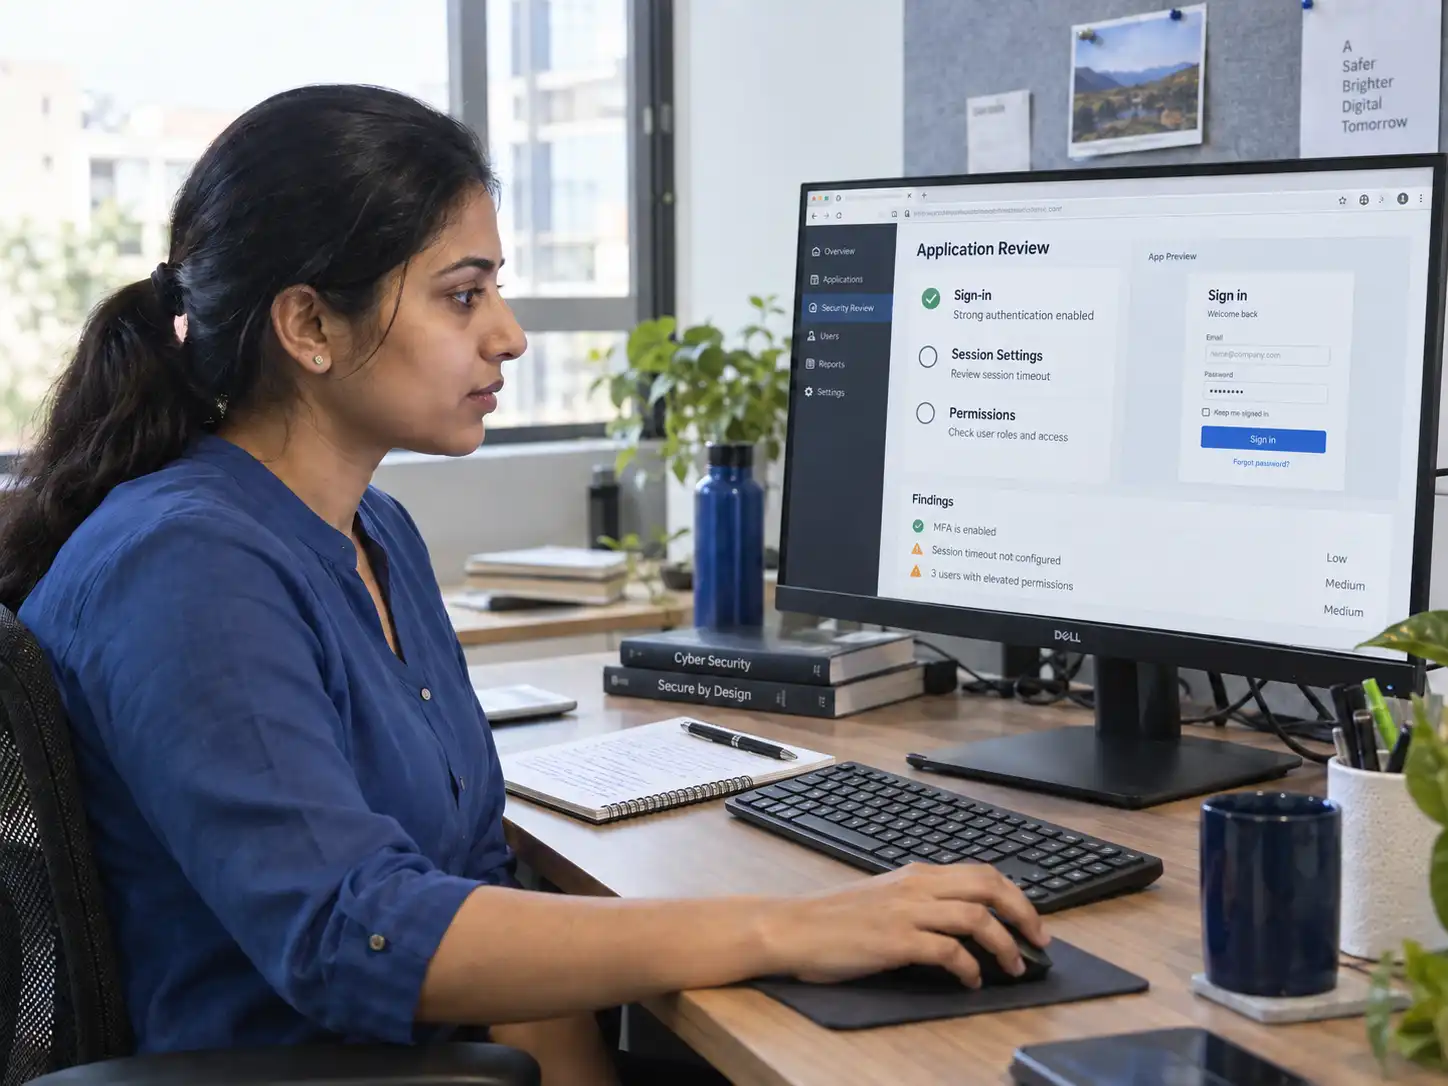
Website & Application Security Review
Review selected sign-in flows, account permissions, input handling, and application settings. Check whether the agreed user roles can access only the records and actions intended for them, and document issues for correction.
Useful for: Businesses preparing a release or reviewing an existing application.
 02
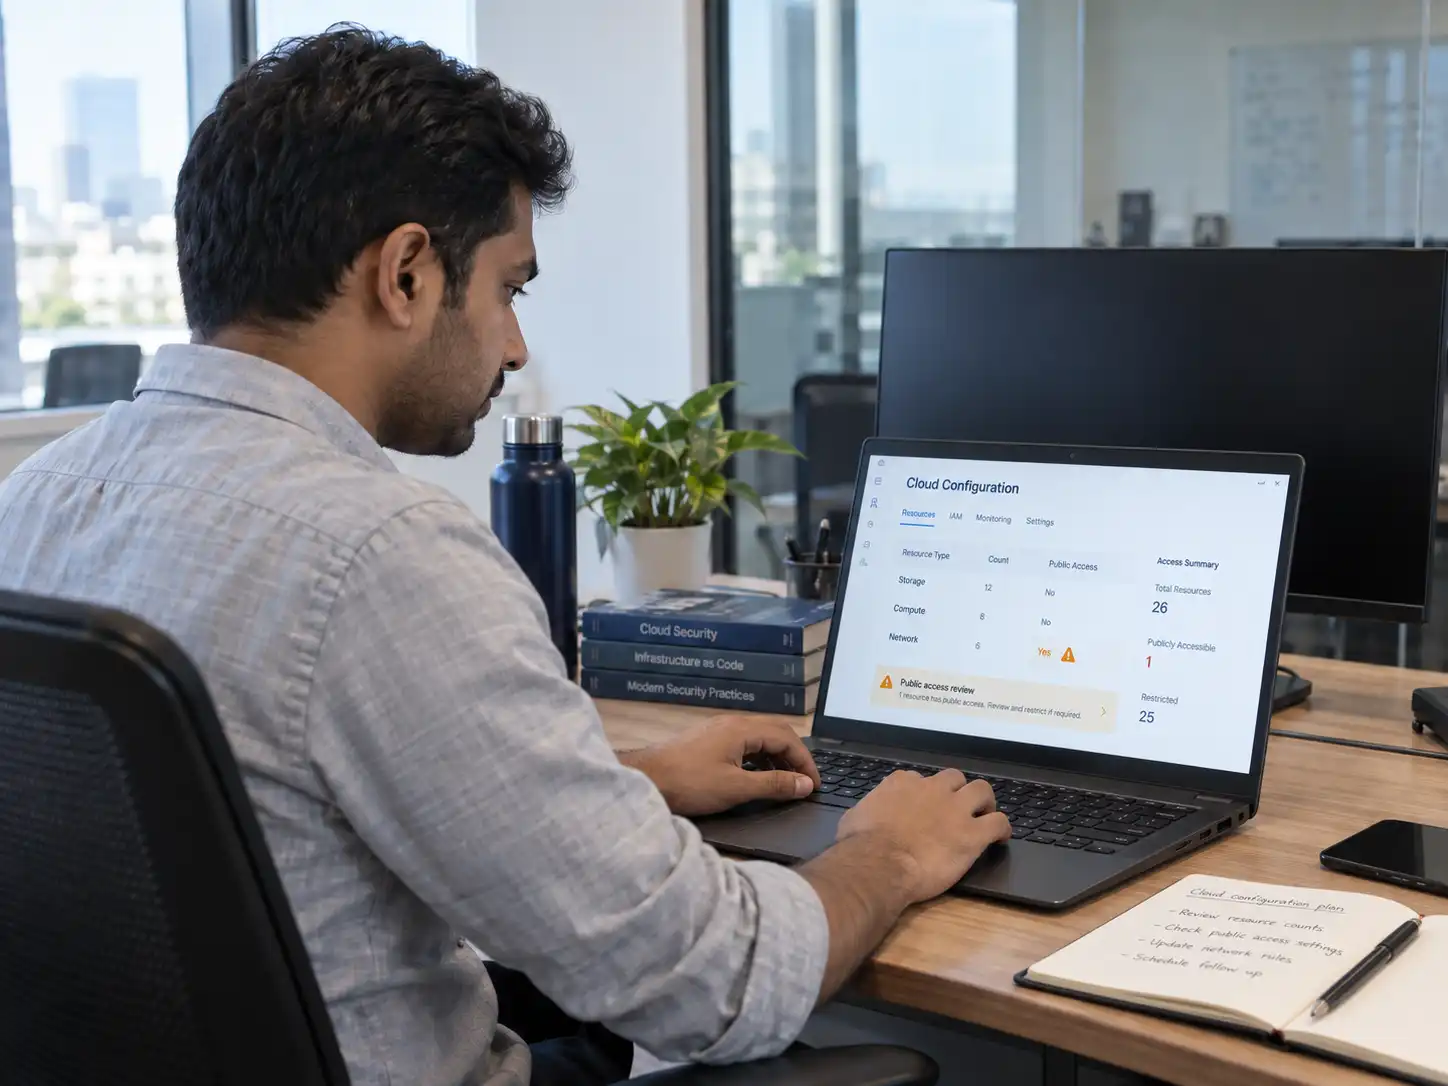
Cloud Configuration Review
Examine agreed cloud resources, administrative permissions, network exposure, and storage access. Identify configuration concerns and plan changes with the people responsible for operating the environment.
Useful for: Teams reviewing a new or established cloud setup.
 03
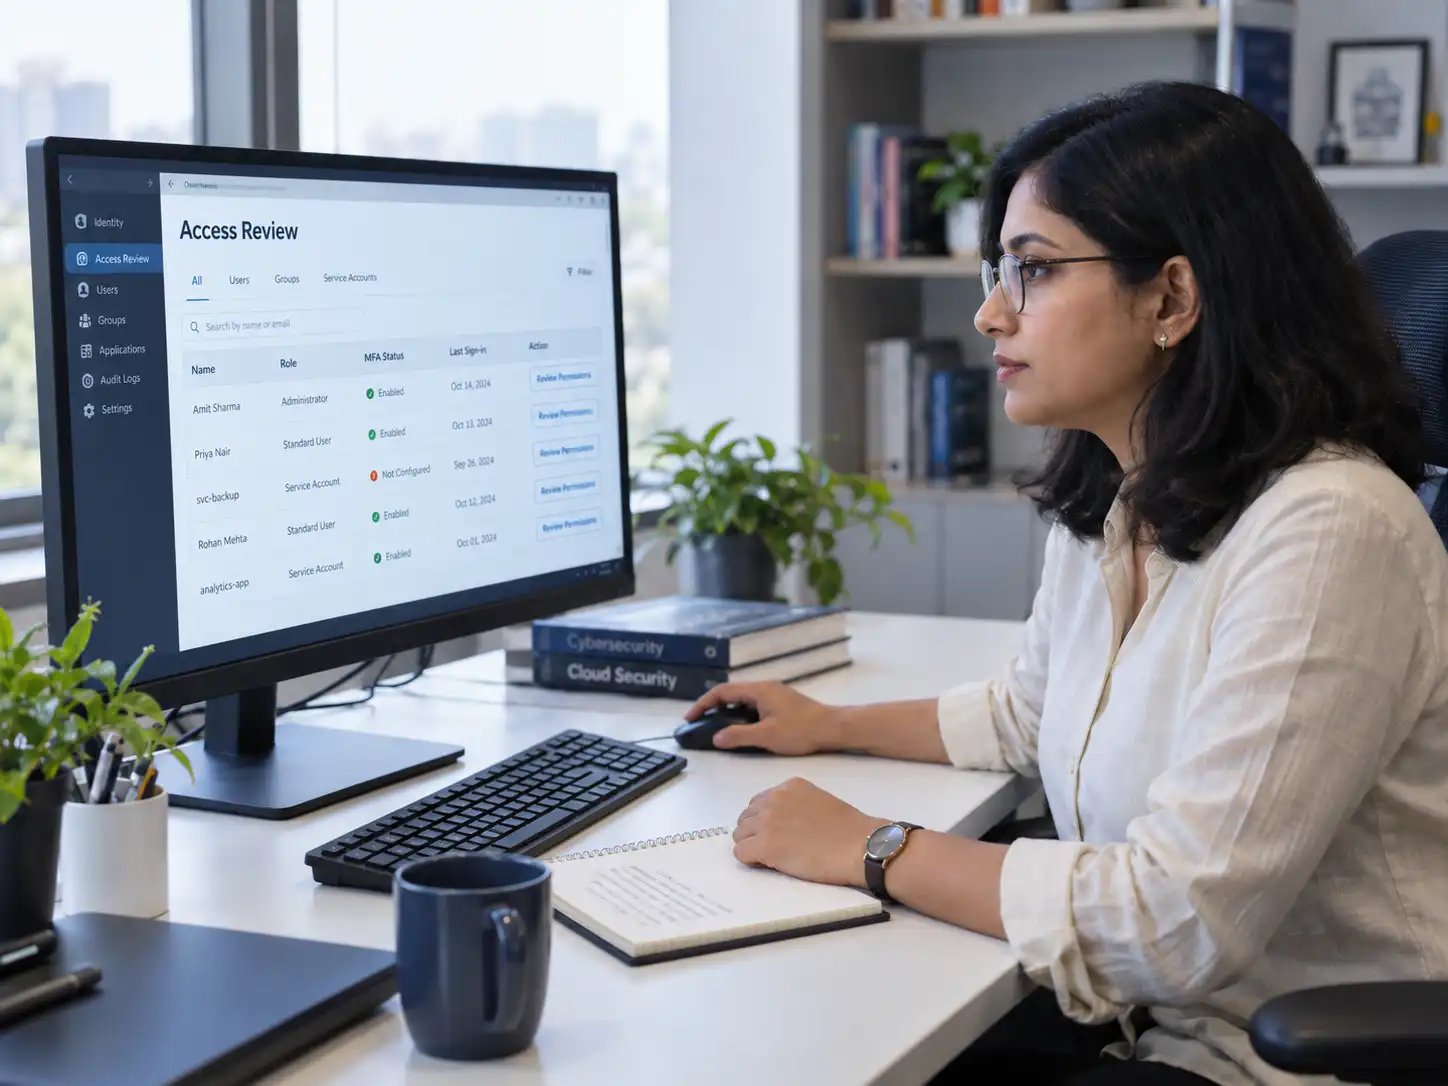
User & Administrative Access Review
Review who has access, what each role can do, and whether accounts still need their assigned privileges. Help define access changes and a repeatable process for users joining, changing roles, or leaving.
Useful for: Organizations with changing teams or shared administrative responsibilities.
 04
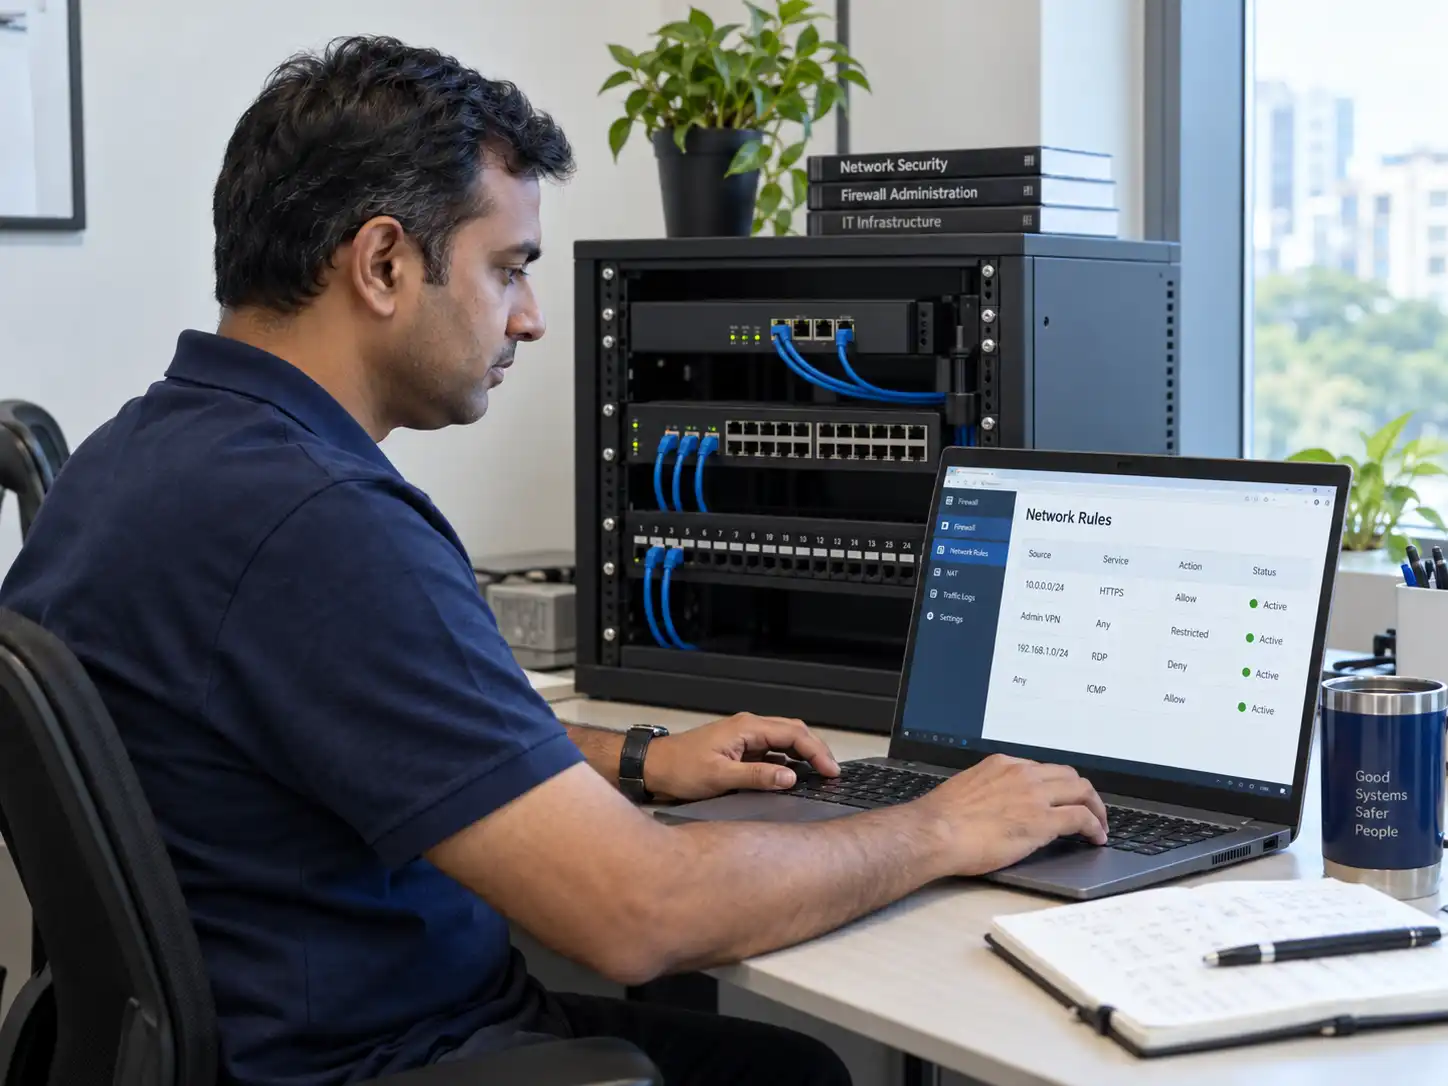
Firewall & Network Access Configuration
Review the connections required between users, applications, and internal services. Refine firewall rules and network separation where appropriate, then check that the required business connections still work.
Useful for: Businesses with exposed servers or multiple connected environments.
 05
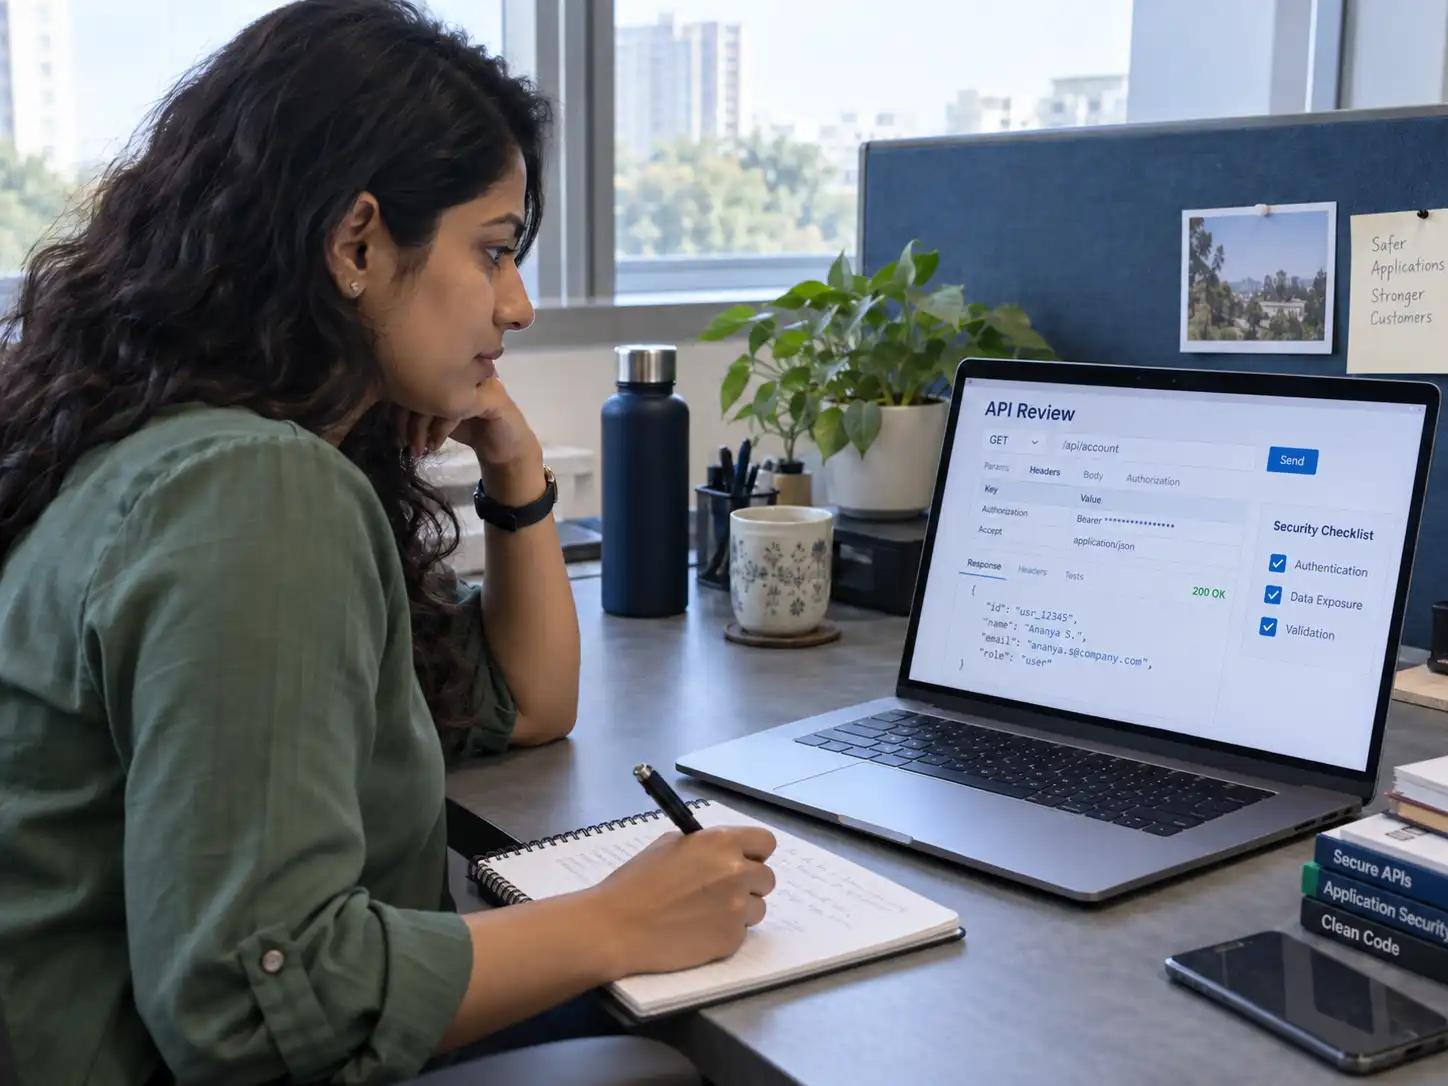
API Access & Data Handling Review
Check selected endpoints for authentication, record-level access, and the information returned in responses. Review request handling and sensitive configuration so integration risks can be addressed alongside application code.
Useful for: Web apps, mobile backends, and connected business systems.
 06
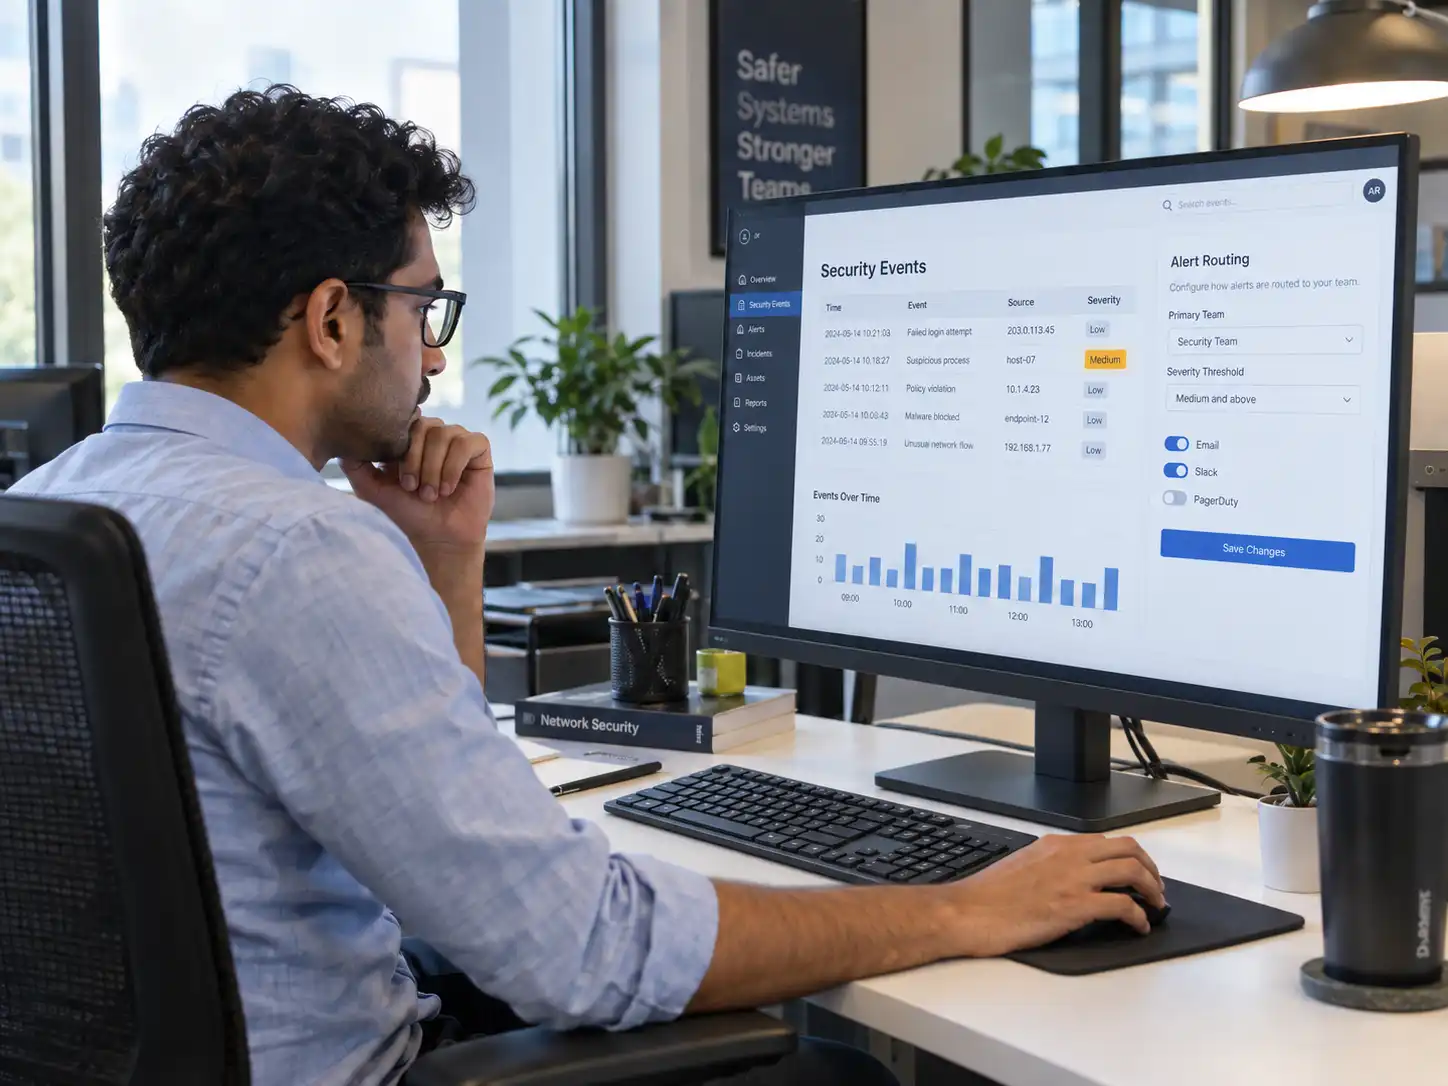
Security Logs & Alert Setup
Identify events worth recording, such as repeated failed sign-ins or administrative changes. Configure available logs and notifications, and define who reviews them and what should happen when an issue is raised.
Useful for: Teams that need better visibility into access and system changes.
 07
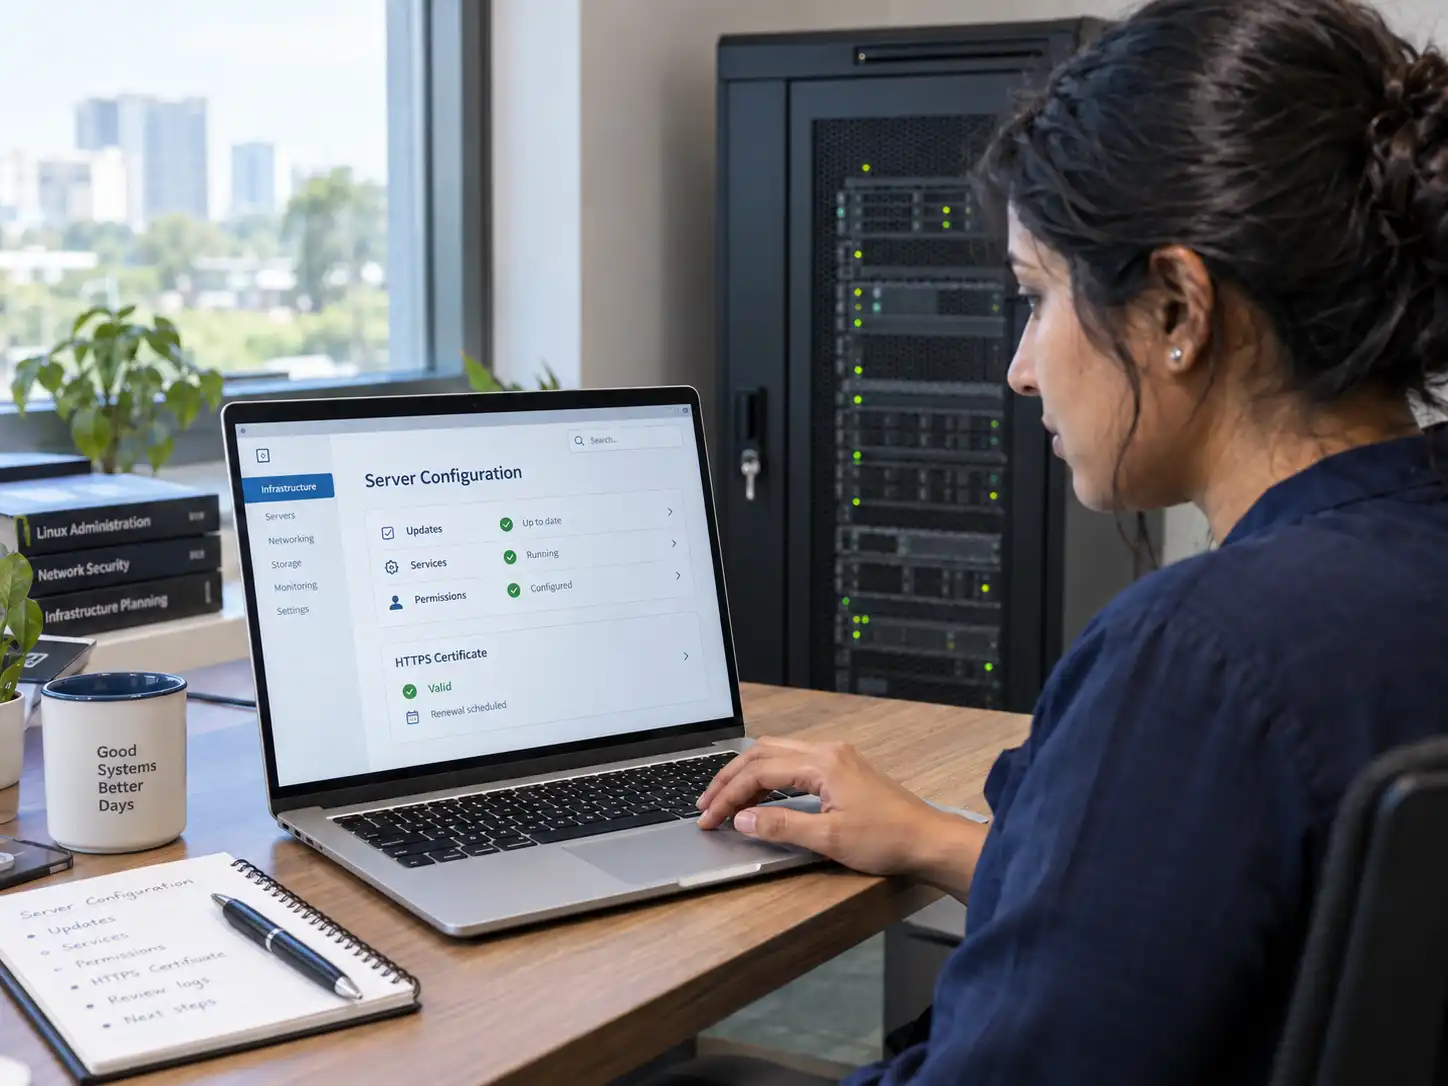
Server Hardening & Certificate Management
Review Linux server access, running services, permissions, and web-server configuration. Include HTTPS certificate setup and renewal checks so these controls have clear ownership and maintenance arrangements.
Useful for: Businesses hosting websites, APIs, and internal applications.
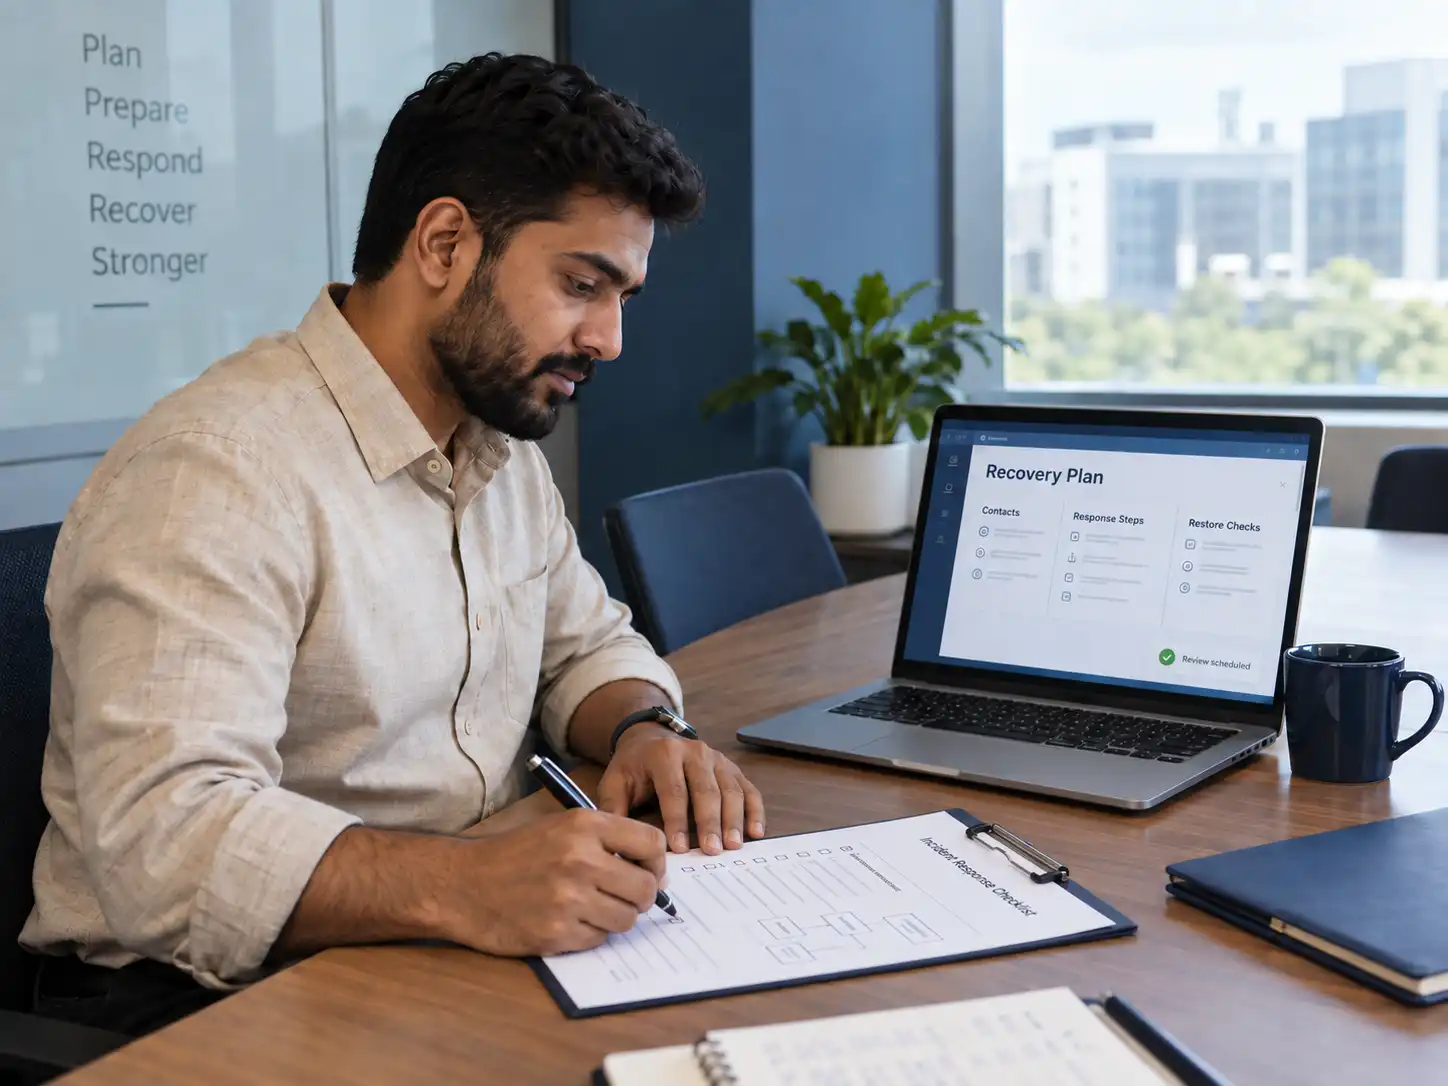 08
Incident Preparation & Recovery Planning
Document the contacts, escalation steps, and recovery responsibilities your team would need during a security event. Review access to relevant logs and backup procedures, and identify where specialist assistance may be needed.
Useful for: Teams establishing a practical plan for handling security concerns.
Have a Specific Security Concern?
Tell us which application or environment is involved and what you want reviewed. We’ll help define the scope, access requirements, and next steps.
How the Controls Fit Together
Review Access from the User to the Underlying System
Security work can span several connected areas. We define which ones are in scope and how findings in one area affect the others.
Who can sign in, which privileges they hold, and how access is managed.
How requests are handled and whether users can perform only permitted actions.
Where agreed information is stored, who can access it, and how it is handled.
Service exposure, communication paths, and administrative configuration.
Available event records, alert routing, and ownership of identified issues.
Business Outcomes
Turn Findings into Work Your Team Can Act On
Clearer Security Priorities
Understand the issues found within scope, their business context, and the recommended order for addressing them.
Reduced Unnecessary Exposure
Address identified gaps in permissions, configurations, and application behavior through approved changes.
Better Control of Access
Make user and administrative privileges easier to review and maintain as responsibilities change.
Documented Follow-Up
Keep a record of findings, changes, validation results, and outstanding actions so the work can be tracked.
Our Approach
Agree the Scope. Review the Findings. Check the Changes.
Define the Review
Confirm the systems, review objectives, permitted activities, access, and working window with the responsible owner.
Assess and Prioritize
Review the agreed areas and document findings with supporting evidence. Discuss business impact and recommended actions with your team.
Implement Approved Improvements
Make the agreed configuration or code changes, with a plan for service impact and rollback where relevant.
Recheck the Affected Areas
Validate the changes against the identified issues and check that the relevant business functions still work. Record what was resolved and what remains open.
Plan Ongoing Review
Define follow-up actions and any recurring reviews, maintenance, or logging support included in the agreement.
Implementation & Support
Keep Security Work Connected to System Changes
New features, accounts, and infrastructure changes can introduce new review needs. We can support approved remediation, access reviews, certificate checks, logging improvements, and configuration updates. Coverage, support hours, and escalation responsibilities are defined around your environment.
Frequently Asked Questions
What to Know Before a Security Review
01What can a security assessment cover?
The scope may include application behavior, APIs, server settings, cloud configuration, network access, user permissions, and selected operating practices. We agree on the systems and review objectives before starting.
02Can you review an existing website or mobile application?
Yes. We can scope a review of selected authentication, permissions, APIs, dependencies, configuration, and data handling. Access to the relevant environment and code, where needed, is agreed with the system owner.
03Can you help implement the fixes?
Yes. Remediation can include agreed code or configuration changes, followed by checks of the affected areas. We separate the assessment findings from implementation work so responsibilities and scope are clear.
04What will we receive after the review?
The agreed deliverables can include a findings report, affected systems, supporting evidence, priorities, and recommended actions. Where remediation is included, we also record changes, recheck results, and unresolved items.
05Will the review disrupt our live systems?
We discuss testing methods, operating constraints, and the working window before beginning. Where an activity could affect service, we plan an appropriate environment or maintenance window with you. Service impact depends on the agreed work.
06Can you configure HTTPS and manage certificates?
We can review certificate installation, HTTPS configuration, and renewal arrangements for the agreed services. Monitoring and ongoing certificate maintenance can be included in the support scope.
07Do you provide continuous monitoring and emergency incident response?
We can scope logging, alert configuration, and agreed review or troubleshooting support. Around-the-clock monitoring or emergency response should not be assumed; coverage, response arrangements, and any need for a specialist provider are discussed separately.
08Does a security review guarantee that our systems are safe?
No. A review covers defined systems and activities at a point in time. The purpose is to identify issues, address agreed gaps, and give your team a clearer basis for ongoing security work.
09Is this a compliance certification service?
This page covers technical reviews and implementation support. A review does not itself provide regulatory approval or certification. If a framework is relevant to your project, its requirements and any specialist assessment work need a separate scope.
010What determines the cost and timeline?
The main factors are the systems involved, access available, depth of review, testing constraints, and whether remediation is included. We provide a proposed scope and schedule after discussing these details.
Let’s Discuss Your Environment
What Would You Like Us to Review?
Share the systems involved, the concerns you have, and any upcoming changes. We’ll help define a focused review and the implementation support you may need.
Discuss Your Security Requirements